
Former Mt. Gox CEO Mark Karpelès criticized Ledger’s response to {hardware} implant warnings, questioning whether or not earlier communication might have prevented losses.
Karpelès stated Ledger acquired studies of spy {hardware} implants as early as December 2025. He accused the agency of responding inadequately.
According to him, Ledger’s solely response was a weblog submit a couple of compromise in March 2026.
For him, Ledger might have executed extra to stop the CryptoBillis incident, the place customers misplaced over $90M.
I do know a greater communication on this on the time might have saved 90+ million USD in losses. I do know it’s a troublesome job, however I can’t fathom how you might have failed to be alarmed by mass-produced superior implants.
On his half, Ledger’s Gauthier learn this as advantage signalling, not real criticism, and referred to as out Karpelès’ previous failure on the Mt. Gox trade.
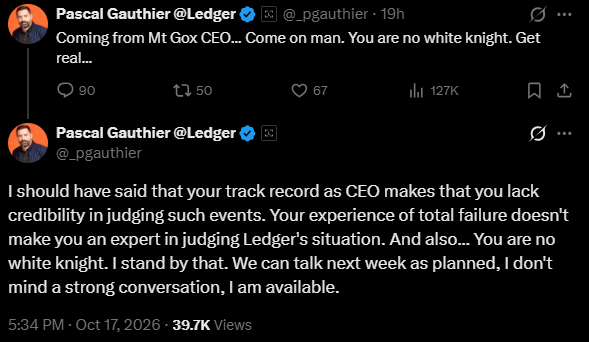
The interplay between the 2 acquired too private and veered off the essential matter: Was the Ledger provide chain compromise and +$90M in stolen funds avoidable?
Community blasts Ledger for sluggish response
Mark Karpelès strongly believes that the unlucky provide chain assault might have been stopped primarily based on the early ‘five-alarm fire’ warnings. While accepting his shortcomings at Mt. Gox, Karpelès added,
I hoped you guys had been higher than that. I’ve been holding Ledger to a better normal than what occurred at Mt. Gox, as a result of I trusted you to do higher by studying of my failure – to be higher than me.
He additionally accused Ledger of “downplaying the incident” as remoted to reseller CryptoBillis, regardless of studies of comparable implants in different areas.
Ledger disputed studies of European exposure after analyzing a reported case in Germany.
However, Karpelès maintained that the assault prolonged additional. He stated he had helped a number of customers examine their gadgets for compromise.
He urged Ledger to present clearer disclosures:
There could be a great cause for that (denying implants in different areas), however an finish person doesn’t know that, and shouldn’t have to fear if their system is altered or not
Surprisingly, the group sided with Karpelès and pressed Ledger for extra transparency.
What does the Ledger assault imply for patrons?
In early October, Ledger confirmed gadgets bought by reseller CryptoBillis had unauthorized implants that scan and ship seed phrases to a personal server. It paused gross sales from CryptoBillis and the broader Southeast Asian area as losses crossed $100M.
As a precaution, a number of gamers within the sector, together with Trezor and OneKey, eliminated third-party resellers and tightened distribution checks.
Crypto was spawned out of mistrust of presidency and centralized entities, with self-custody as its basis to give customers full management over their belongings. But with ongoing self-custody safety dangers, extra might be compelled to return to safer centralized custodians.
Final Summary
- Mt. Gox CEO blasted Ledger for ‘downplaying’ its provide chain assault
- Ledger maintains the compromise is remoted to the Southeast Asian area, however others declare the assault is world